
All How to Integrate a Payment Gateway: Shopify, Magento, and Custom Stores
July 29, 202615 min read

Optimizing transaction completion is one of the most critical financial levers a digital merchant has. Recent multi-industry benchmarks put the global average cart abandonment rate at a stubborn 70.22%.
Mobile commerce, despite capturing most digital storefront traffic, sees an even higher abandonment rate of 73% to 85.65%, driven by form-entry friction, sluggish network latency on checkout pages, and visual interface distractions.
An optimized ecommerce payment solution pays off. Checkout usability improvements can capture a share of the estimated $260 billion in recoverable revenue across the US and European markets each year. A high-performance ecommerce payment processing flow reduces transaction friction and is a primary driver of customer lifetime value and conversion.
This article covers what a payment gateway is and how to integrate a payment gateway in 2027.
What Is a Payment Gateway in eCommerce
A payment gateway is the secure, encrypted bridge transmitting transactional data between the consumer's browser and the acquiring financial institution. Three entities operate within this transaction lifecycle, each with a distinct role:
- Payment Gateway.
The software layer responsible for capturing, encrypting, and securely transmitting cardholder data from the merchant's storefront to the payment processor. It also verifies that transaction details are formatted correctly.
- Payment Processor.
The financial institution operating in the background that routes encrypted card data through the card networks (Visa, Mastercard, American Express). It communicates with the issuing bank (the customer's bank) and the acquiring bank (the merchant's bank) to clear and settle funds.
- Payment Service Provider (PSP).
A provider that packages both the gateway and backend processing under a single commercial contract and API. Stripe, Adyen, and Braintree are examples.
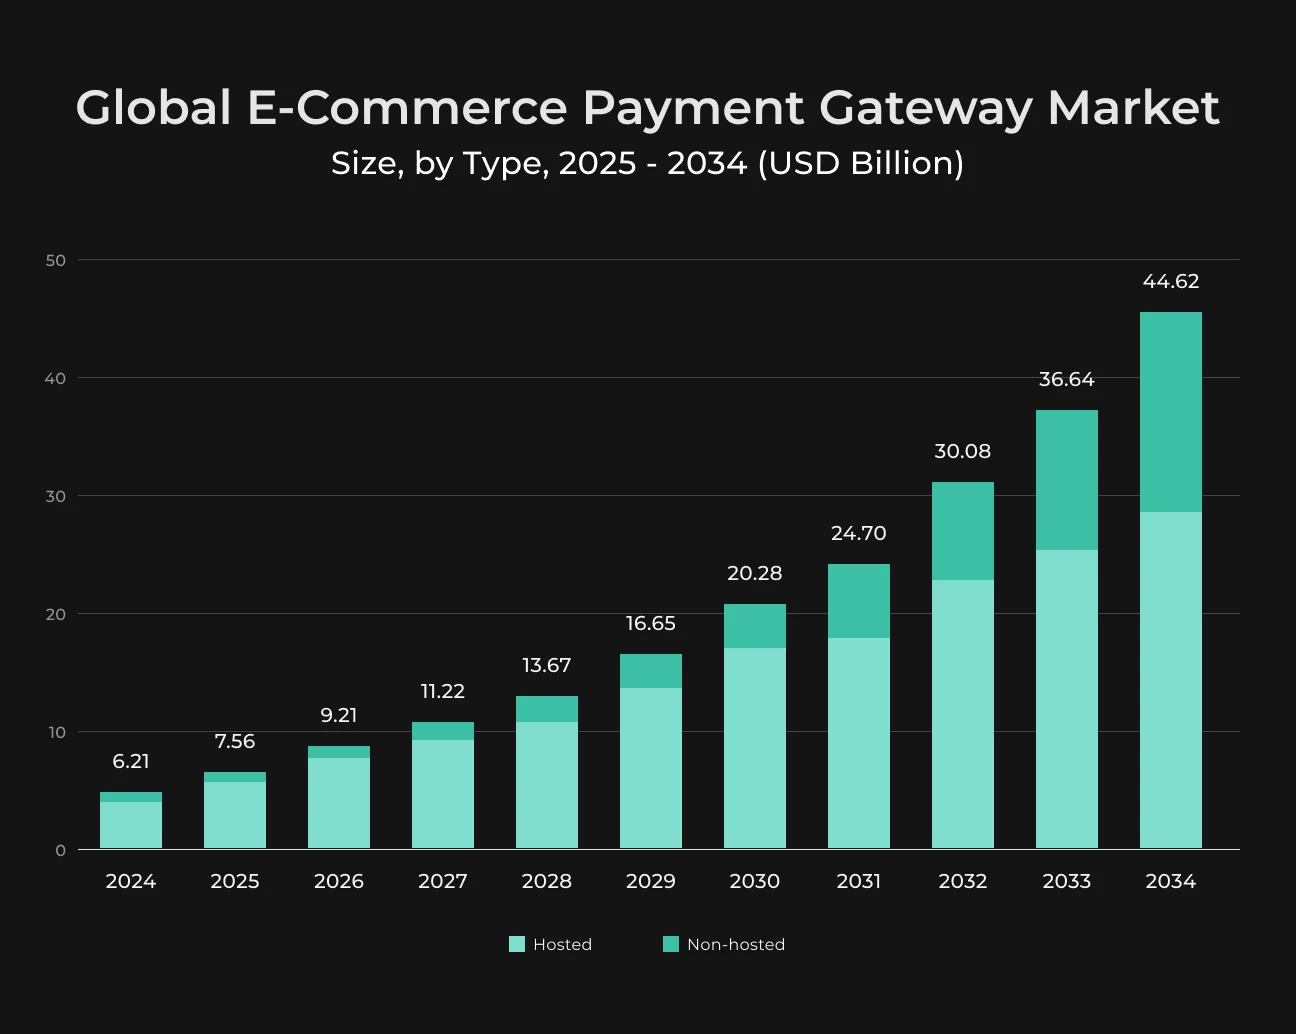
At the programmatic level, supporting diverse ecommerce payment methods extends far beyond merely accepting credit and debit cards. In global commerce, a comprehensive checkout must support alternative payment instruments, including:
- Digital wallets like Apple Pay and Google Pay;
- Direct bank transfers like SEPA and ACH;
- Local wallets;
- Cards;
- Buy Now Pay Later (BNPL) options like Shop Pay Installments, Klarna, or Affirm.
Each payment instrument runs on its own financial rails, so you either build and maintain point-to-point connections for every method or implement a unified ecommerce payment system that abstracts these downstreams into a single API wrapper.
How Payment Gateway Integration Works
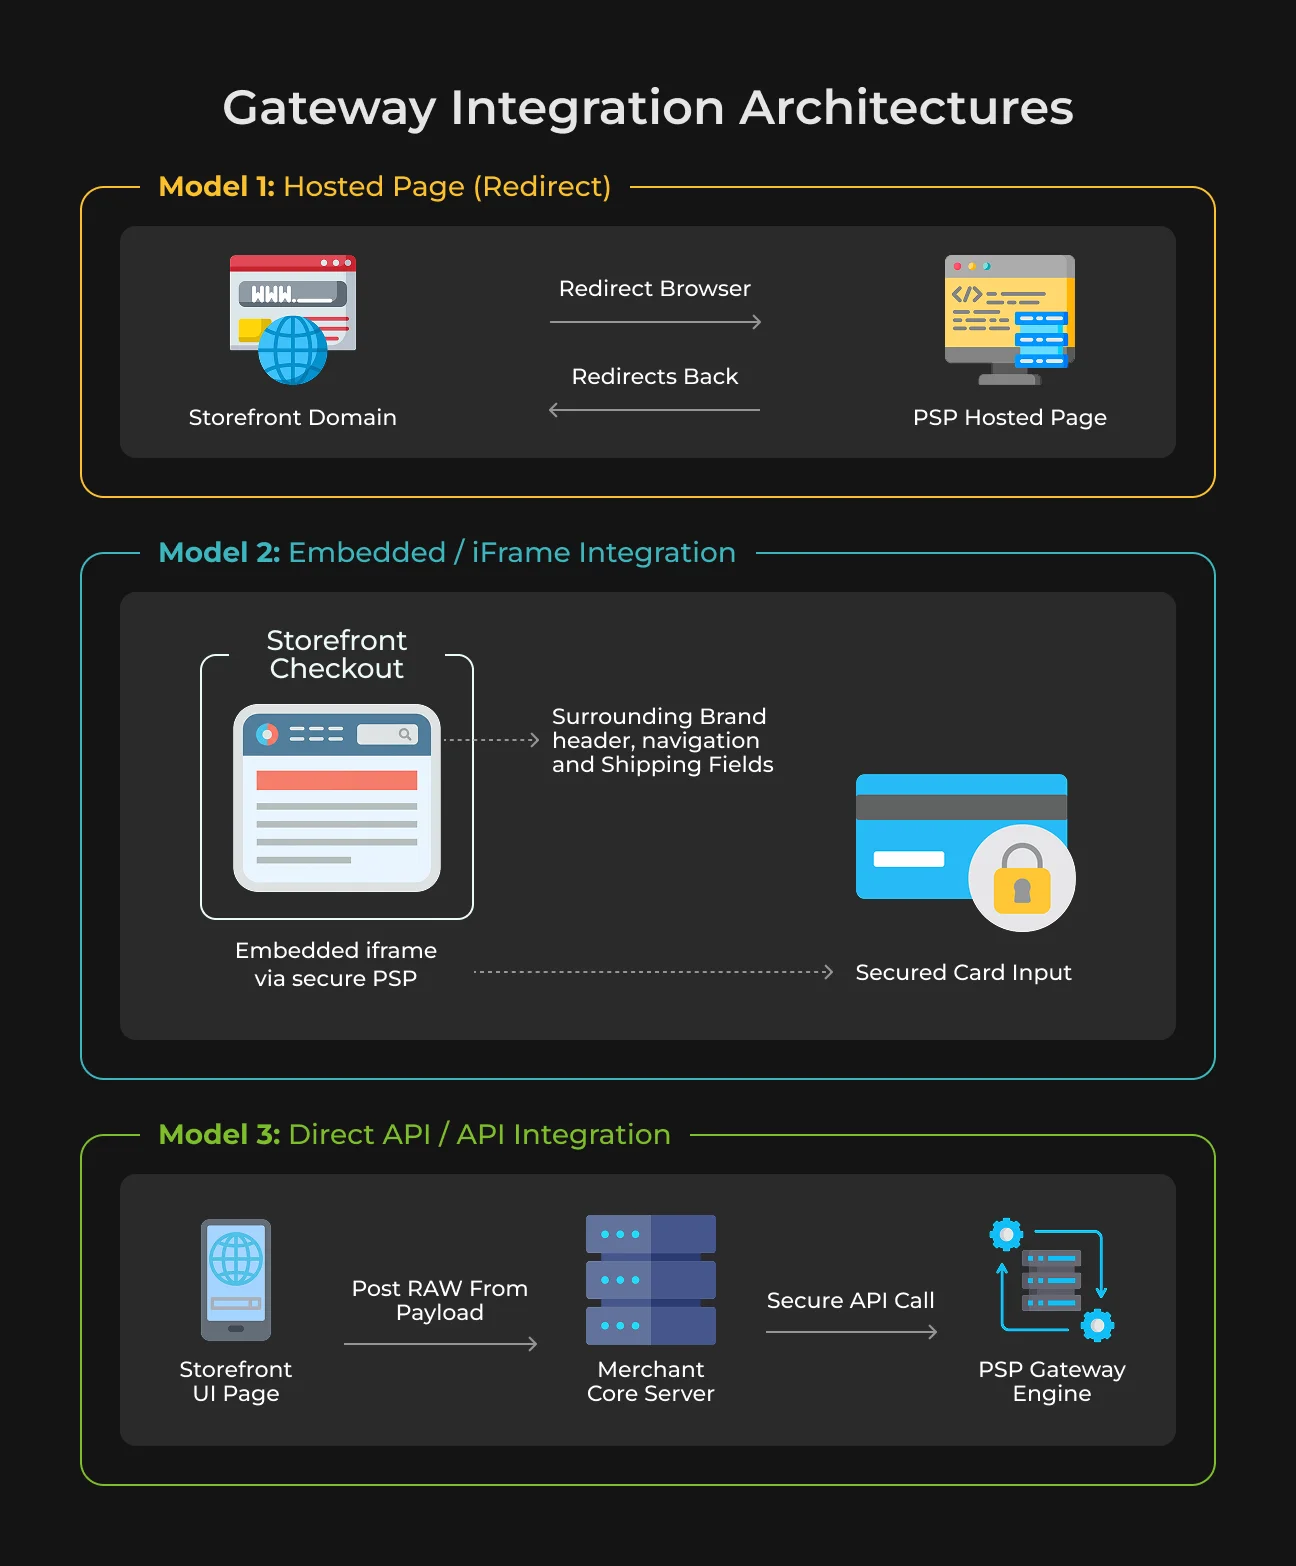
Implementing an online payment gateway integration typically relies on one of three structural patterns, each with a different trade-off between compliance liability, brand continuity, and development complexity.
Model 1: Hosted payment page (redirect)
The storefront redirects the browser off the merchant's domain to a secure payment page hosted by the PSP, then redirects back once the transaction is authorized.
This minimizes security liability and qualifies the merchant for the simplest PCI DSS validation (SAQ A, 22 requirements). It also introduces visual friction and an external redirect that can drive abandonment.
Model 2: Embedded / iFrame integration
This payment processing integration approach embeds secure input fields hosted by the PSP directly inside the merchant's checkout layout, so the customer never leaves the store's domain.
Cardholder data goes straight to the PSP's servers, but malicious scripts on the parent page can still access or manipulate the iframe. That risk pushes compliance up to the more extensive SAQ A-EP standard, roughly 191 security controls.
Model 3: Direct Payment Gateway API integration
Within this payment gateway API integration model, the merchant builds a native payment form on their own domain, collects card data on their application servers, and submits it to the processor via API calls.
This gives complete control over the checkout experience, but puts the merchant's entire server infrastructure in scope for full PCI DSS compliance (SAQ D) and the technical, physical, and administrative audits that come with it.
Integration Dimension | Hosted Payment Page (Redirect) | Embedded / iFrame Integration | Direct API Integration |
| Checkout Continuity | Low; breaks checkout flow by redirecting to an external domain. | High; fields are embedded directly inside the merchant's design. | Maximum; complete control over every element, field, and state transition. |
| PCI Compliance Scope | SAQ A (22 requirements); merchant servers are isolated from card data. | SAQ A-EP (191 requirements); requires vulnerability scanning. | SAQ D (300+ requirements); requires full infrastructure audits. |
| Vulnerability to Keylogging | Low; handled within the PSP's secure ecosystem. | Medium; compromised parent-page scripts can attempt to intercept inputs. | High; payment data resides in the application memory of the merchant server. |
| Development Complexity | Low; typically requires simple JavaScript redirects or ready plugins. | Medium; requires importing SDK scripts and styling custom embedded inputs. | High; requires custom endpoint construction, secure token handlers, and state management. |
| Ideal Use Case | Small merchants with limited technical staff and low transaction volumes. | Mid-market DTC brands looking for seamless UX with manageable compliance work. | Enterprise merchants with dedicated security teams and complex routing requirements. |
How to Integrate a Payment Gateway in Your Store
Successfully implementing an ecommerce payment integration depends on selecting the model that best matches the store's architecture, transaction volume, and operational needs.
Integrating a Payment Gateway in Shopify
For standard DTC brands, setting up a Shopify payment gateway is an easy path.
Shopify Payments, built on Stripe's core infrastructure, eliminates additional platform transaction fees and includes built-in fraud screening. It also enables Shop Pay, which can push checkout completion rates up to 1.72 times higher than standard guest checkout.
However, scaling merchants frequently encounter architectural constraints:
- Third-Party Surcharges.
If an enterprise chooses to route payments through an external processor (such as direct Stripe, Braintree, or regional providers), Shopify levies a third-party transaction surcharge on every sale. This surcharge scales from 2.0% on the Basic plan down to 0.2% on Shopify Plus.
- Locked Checkout Customization.
Shopify limits structural modifications to its checkout pages for merchants below the Shopify Plus tier, restricting the ability to build custom multi-currency routing.
- B2B Integration Friction.
Complex business-to-business processes often require external apps that can lead to data synchronization issues with the core ERP or OMS. Examples of such complex business-to-business processes are net payment terms, automated purchase orders, and localized multi-currency invoicing.
Shopify Subscription Tier | Monthly Subscription Cost | Standard Domestic Card Rate | Third-Party Surcharge Surcharge | Total Cost on $100 Sale (With Stripe) |
| Basic Shopify | $39 ($29 under Annual Billing). | 2.9% + 30¢. | 2.0%. | $5.20 (Gateway's 2.9% + 30¢ + Shopify's 2%). |
| Shopify (Grow) | $105 ($79 under Annual Billing). | 2.7% + 30¢. | 1.0%. | $4.00 (Gateway's 2.7% + 30¢ + Shopify's 1%). |
| Advanced Shopify | $399 ($299 under Annual Billing). | 2.5% + 30¢. | 0.6% (or 0.5%). | $3.40 (Gateway's 2.5% + 30¢ + Shopify's 0.6%). |
| Shopify Plus | From $2,300 (3-Yr Term) / $2,500 (1-Yr). | ~2.15% + 30¢ (Negotiable). | 0.2%. | $2.65 (Gateway's 2.15% + 30¢ + Shopify's 0.2%). |
Integrating a Payment Gateway in Magento
A Magento payment gateway integration is one of the more technically involved jobs in digital commerce.
Adobe Commerce/Magento runs on a highly modular backend, with infrastructure requirements that also make specialized Magento hosting important for production environments. While it ships with native integrations for PayPal and Braintree, adding external gateways means building or installing a dedicated Magento payment module.
Key technical considerations for Magento environments include:
- 3DS2 Integration.
Unlike SaaS platforms that handle authentication out of the box, 3-D Secure 2.0 telemetry and challenge states have to be built directly into Magento's checkout JavaScript layers.
- Partial Captures and Credit Memos.
Handling partial captures as items ship, and running partial automated refunds, requires aligning the gateway's API with Magento's internal sales and invoice schemas.
- Tokenized Vaults.
Storing credentials for return customers means using Magento's native Vault modules to tokenize on the gateway side, so raw card data never touches the database.
- Multi-Storefront Scoping.
Enterprises running multiple regional storefronts need separate merchant IDs and currencies configured at the individual Store View level, or they'll incur unintended currency conversion fees.
This calls for a dedicated Magento backend specialist, not a generalist developer.
They'll need to work with Magento's Dependency Injection system, its plugin/interceptor patterns, and its quote-to-order state transitions. That means writing XML configs in etc/payment.xml to define the payment methods, then wiring up the dependencies in etc/di.xml using the Payment Method Facade.
Custom Payment Gateway Integration
Headless architectures and custom systems built on Laravel, Node.js, or Django don't have pre-built payment modules. Every deployment is a custom API integration built from scratch, which gives developers complete architectural control to design finely tuned checkout experiences.
The trade-off is that the development team owns every workflow and edge case.
- Multi-Gateway Fallback Routing. Rule-based routing to redirect transactions during outages or optimize processing fees, say routing European transactions to Adyen and US transactions to Stripe.
- Decoupled Vaulting. Independent credit card vaulting so the merchant can switch processors without losing historical tokenized data.
- Bidirectional Syncing. Real-time APIs that push transaction states, cancellations, and partial adjustments across the storefront, ERP, and warehouse platforms.
Schedule Your Free Payment Consultation
Talk to our engineers about the right integration model, PCI scope, and processor mix for your store.
Common Integration Problems and How to Solve Them
SapientPro’s team sees four main integration problems arise again and again in ecommerce payment processing.
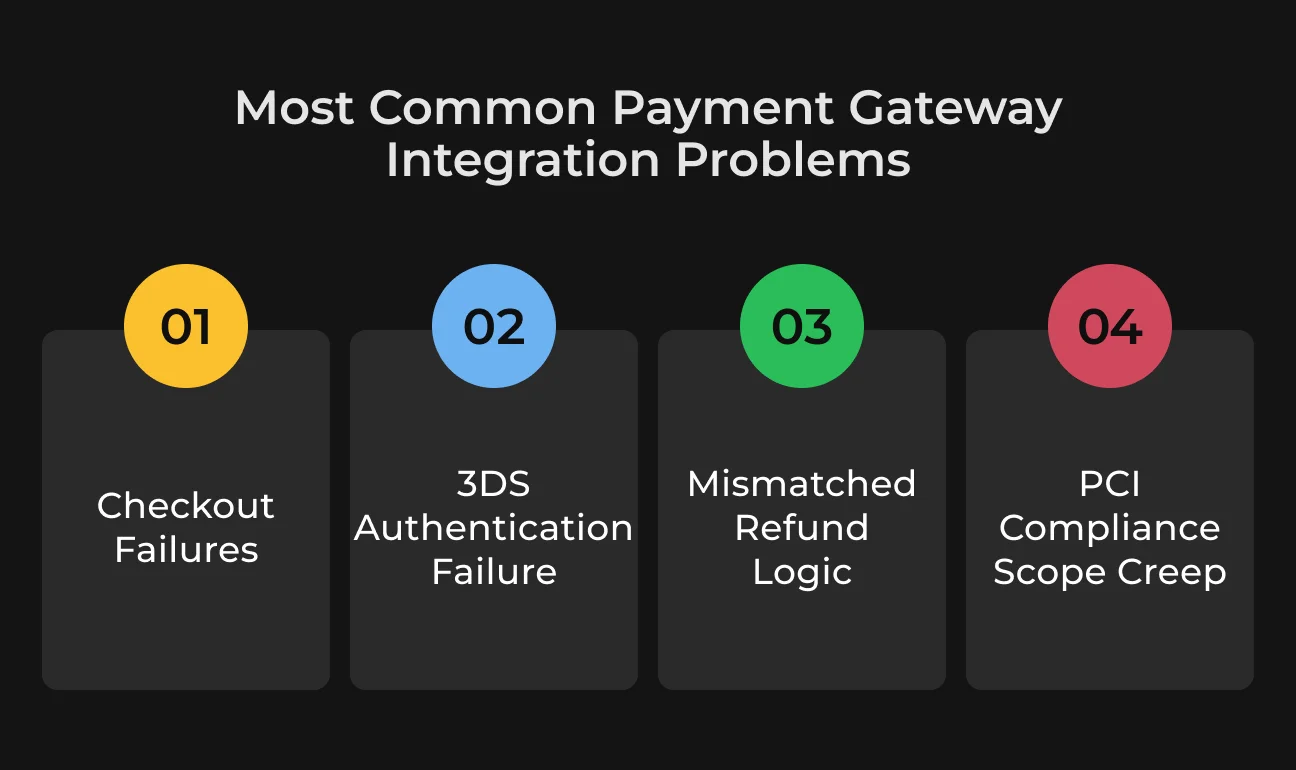
1. Checkout Failures
Systemic errors inside checkout applications lead directly to abandoned purchases and lost revenue. The following table shows common checkout failures and how to address them within your payment gateway for ecommerce site.
Failure Category | What It Looks Like |
| Soft Declines | Temporary decline from insufficient funds, a bank velocity block, or a network timeout |
| Hard Declines | Permanent decline from an expired, stolen, or lost card |
| API Webhook Failures | Missed or delayed payment status notifications between gateway and storefront |
| Credential Mismatches | Expired or environment-mismatched API keys that freeze checkout |
| Aggressive Fraud Rules | Misconfigured risk filters blocking legitimate high-value orders |
Soft Declines
These are usually tied to ISO code 51 (insufficient funds), bank-side velocity blocks, or plain network timeouts. The customer just sees a generic “Transaction Declined” message with no hint that trying again in a few minutes might work. Build intelligent routing that automatically retries the charge through a backup processor before writing off the sale.
Hard Declines
ISO code 54 (expired card) and codes 43 and 41 (stolen or lost cards) mean the card genuinely can't be charged. Prompt the customer to check their details or switch payment methods, and add a card-updater service that refreshes expired card data before it becomes a problem at checkout.
API Webhook Failures
Latency, server timeouts, or a webhook that never arrives can leave a customer charged while the storefront shows no confirmation. That gap generates support tickets and, worse, duplicate shipments if nobody catches it. Idempotent API endpoints, webhook retry queues, and a fallback polling job that checks payment status directly with the gateway close this gap.
Credential Mismatches
An expired, rotated, or environment-mismatched API key, a sandbox key still live in production, for example, freezes checkout entirely and returns 400 Bad Request errors at the worst possible moment. Keep test and production credentials in strictly separated environment variables, and rotate keys through a process that updates every environment at once.
Aggressive Fraud Rules
Overly strict risk filters flag legitimate high-value buyers as fraud and block them with no explanation. Machine-learning-based fraud filtering that weighs richer context, order history, device signals, and address consistency, catching actual fraud without punishing your best customers.
2. 3DS Authentication Failure
Strong Customer Authentication (SCA) rules in the UK and European Economic Area require 3-D Secure 2 (3DS2) for electronic transactions.
The protocol verifies identity using device, location, and transaction context, and if a transaction is flagged, prompts the customer with a challenge flow such as biometrics or a one-time passcode. Since these prompts increase cart abandonment, maximizing frictionless approvals is a core conversion lever.
Unnecessary challenges usually happen because a merchant submits incomplete authentication data. When you build a 3DS2 integration, populate every supported parameter in the EMVCo-specified Authentication Request (AReq):
- Device channel parameters;
- Browser metadata;
- Exact billing addresses;
- Historical account telemetry.
A rich data payload gives issuing banks enough context to authorize transactions silently, protecting both conversion and the liability shift that shields merchants from chargeback fraud.
As compliance frameworks move toward PSD3, plan to support emerging features too, including delegated biometric authentication, Pay-by-Bank Open Banking interfaces, and accessibility-driven SCA exemptions.
3. Mismatched Refund Logic
Discrepancies between storefront records and backend ERP/OMS ledgers are a real source of operational friction and financial leakage.
If a storefront logs a successful refund but the data doesn't sync cleanly with the central ERP, someone has to close the ledger manually. These mismatches usually come from system-to-system handoff failures, not errors in the payment gateway itself.
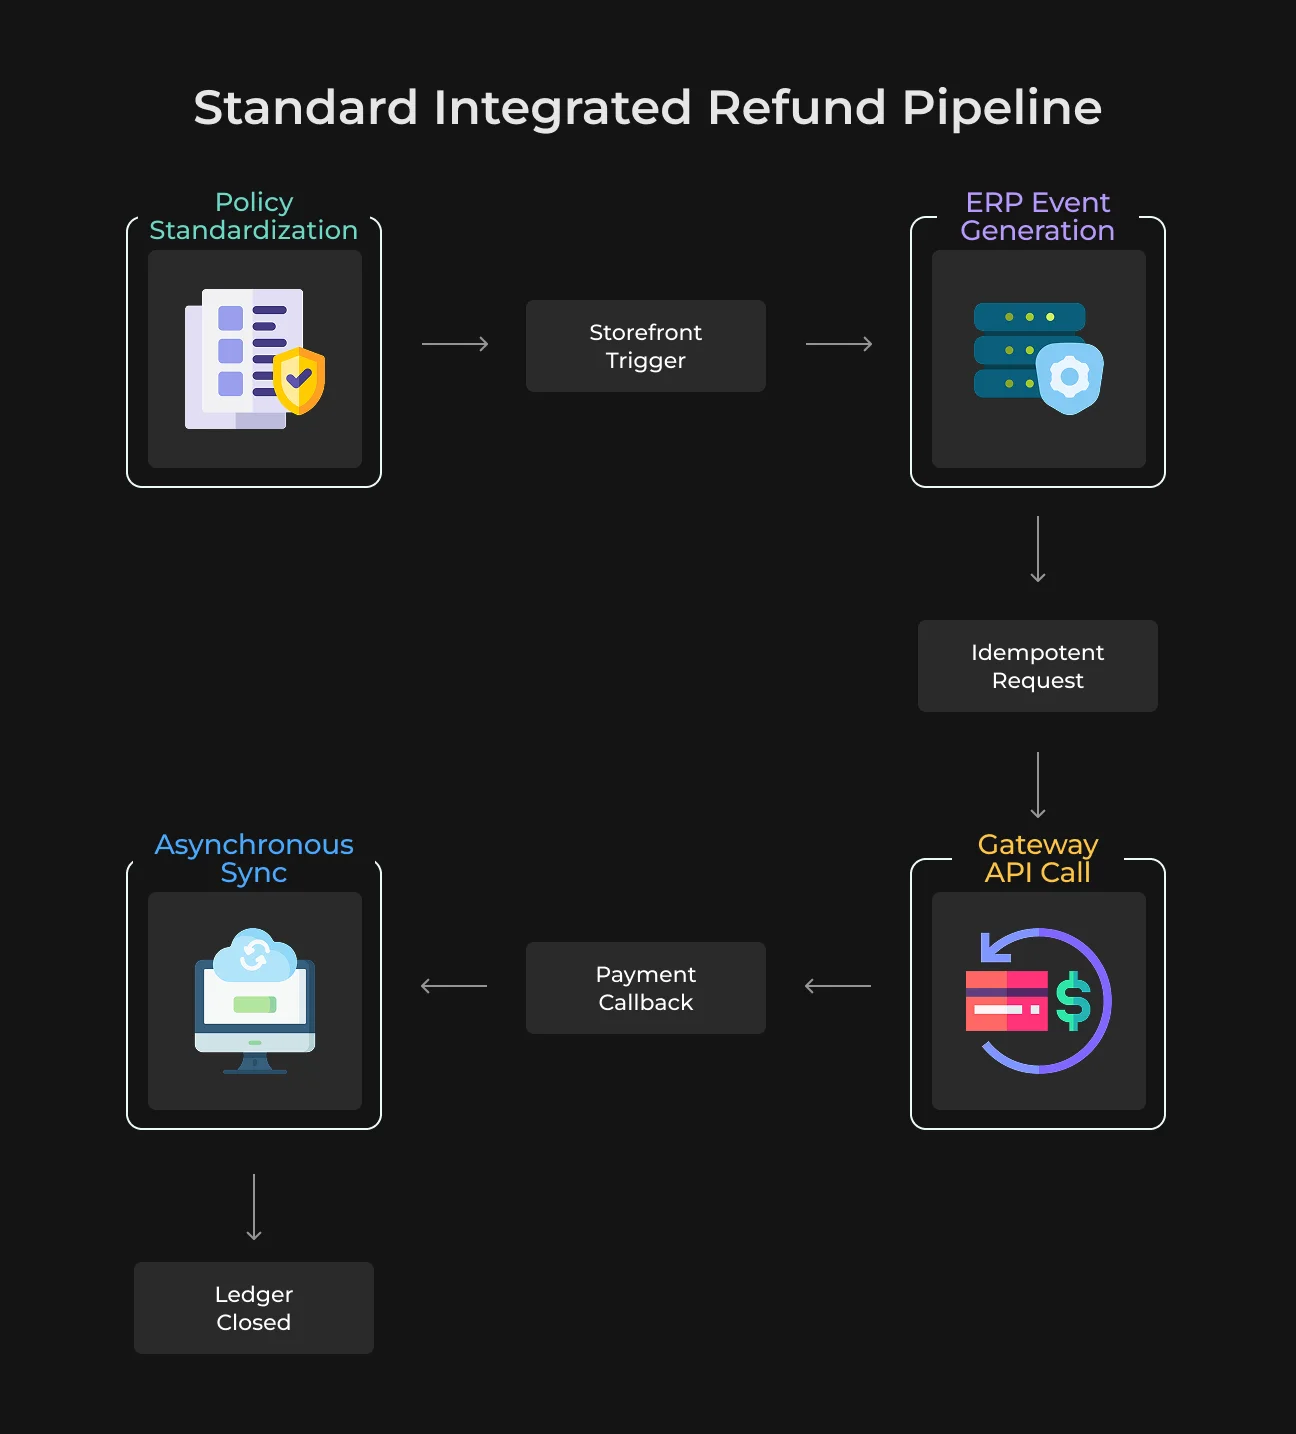
An automated refund pipeline fixes this:
- Standardize policy rules. Define strict, standardized return reason codes (damaged in transit, wrong item shipped, customer cancellation) across the storefront and ERP;
- Generate events in the ERP first. Start accounting events inside the ERP or OMS so an audit trail exists before any money moves;
- Use idempotent gateway API calls. Connect the ERP directly to the gateway, and issue refunds with explicit idempotent keys to prevent duplicate payouts;
- Sync state asynchronously. Build listeners that watch gateway state transitions (submitted, pending, completed, failed) and write them back to the ERP automatically.
Done right, this workflow cuts down on return fraud and shipping losses.
4. PCI Compliance Scope Creep
Many merchants unintentionally pull unexpected parts of their hosting infrastructure into PCI DSS audit scope. Direct API calls that process card data on the application servers are the usual culprits.
Designing around embedded iframes or hosted redirects keeps compliance overhead down. In an iframe setup, sensitive fields are served directly from the PSP's secure servers, so cardholder data never touches the merchant's infrastructure.
That said, an iframe doesn't fully remove compliance obligations.
Direct data exposure is reduced, but malicious scripts injected on the parent page can still tamper with the iframe source or log keystrokes. That's why embedded iframe checkouts fall under the more extensive SAQ A-EP standard (191 controls) rather than the basic SAQ A standard (22 controls) used for hosted redirects.
Securing an iframe setup means:
- Implementing strict Content Security Policies (CSP);
- Applying sandbox attributes to the iframe;
- Running regular vulnerability scans across all store domains.
Payment Gateway Security Risks and How to Handle Them
Security risks in payment gateway integration don't stop at PCI DSS scope for the checkout page. Once a gateway goes live, sensitive data can leak into places nobody's watching, and rushed fixes on the operations side create their own vulnerabilities.
Cardholder Data Leaking Into Logs and Backups
Debug logs are the usual culprits. A developer troubleshooting a failed transaction turns on verbose logging, and full card numbers or CVVs end up sitting in plaintext log files, error tracking tools, or database backups nobody flagged as in-scope. Once that data exists outside the payment gateway's secure environment, it's a PCI violation and a breach risk, no matter how solid the checkout integration itself is.
Log Redaction and Data Masking for PCI Compliance
Configure logging middleware to strip or mask PANs, CVVs, and full track data before anything gets written to disk. Apply the same masking rules to error monitoring tools like Sentry or Datadog, and confirm database backups capture tokens only, never raw card data.
Weak Tokenization and Card Vaulting
Storing card details for repeat customers means real tokenization, not just hiding the number behind a UI mask. A vault that stores a reversible or weakly encrypted version of the card isn't meaningfully different from storing the card itself, and it puts the merchant back into a heavier PCI DSS scope than intended.
Secure Card Vaulting for Repeat Customer Payments
Use vaulting provided by the gateway or PSP, so the token lives only in a system already scoped for PCI DSS, and the merchant's own database holds nothing but a non-reversible reference. Rotate vault encryption keys on a set schedule, and restrict which services are allowed to call the detokenization endpoint.
Chargeback and Dispute Mishandling
Manual chargeback handling doesn't scale. When dispute volume climbs, missed evidence deadlines and inconsistent responses get expensive fast: banks assign the merchant a higher risk rating, and gateways start reserving funds or raising processing rates.
Automated Chargeback and Dispute Response Workflows
Pulling order data, shipping confirmations, and customer communication logs into a single dispute package automatically cuts response time and stops deadlines from slipping. Route disputes above a set dollar threshold to a human reviewer, and track win and loss rates by decline reason to catch systemic issues, like a fraud filter that's too aggressive, before they compound.
Exposed or Stale API Credentials
API keys and webhook secrets sitting in source control, shared Slack messages, or old employee accounts are some of the more common ways payment infrastructure gets compromised. A key doesn't need to be stolen through a sophisticated attack. It just needs to still work after it should have been revoked.
API Key Rotation and Secrets Management for Payment Gateways
Store keys in a dedicated secrets manager rather than in environment files or config repos, and rotate them on a fixed schedule instead of only after an incident. Set up alerts for API calls from unrecognized IP ranges or unusual patterns, and cut off access immediately when an employee or vendor relationship ends.
Why Handle Payment Gateway Integration to SapientPro
SapientPro is a custom software development agency that has been designing, deploying, and maintaining high-performance ecommerce platforms, custom payment integrations, and real-time transaction engines since 2017.
Instead of working from rigid templates, we build gateway architecture around the enterprise's actual operational flows, which cuts out system silos and avoids costly refactoring down the line.
Partnering with SapientPro gets you:
- Reduced Compliance Overhead. Enterprise-grade implementations aligned with GDPR, ISO, and PCI DSS parameters, minimizing audit exposure.
- Seamless Omnichannel Synchronization. SapientPro's POS terminal for Magento keeps stock and ledger reconciliation in sync across physical and online channels, with offline transaction processing via a local database cache so outages don't cost you sales.
- Revenue Protection. Advanced 3DS2 telemetry, multi-processor smart routing, and dependable state-synchronization wrappers that stop silent checkout dropouts and recover lost carts.
SapientPro handles full-cycle payment gateway development and custom API integration to keep your checkout secure and frictionless. Schedule your free payment consultation today.
Fix Your Checkout Failures Today
Let our team diagnose declined transactions, webhook gaps, and fraud filter issues costing you revenue right now.


